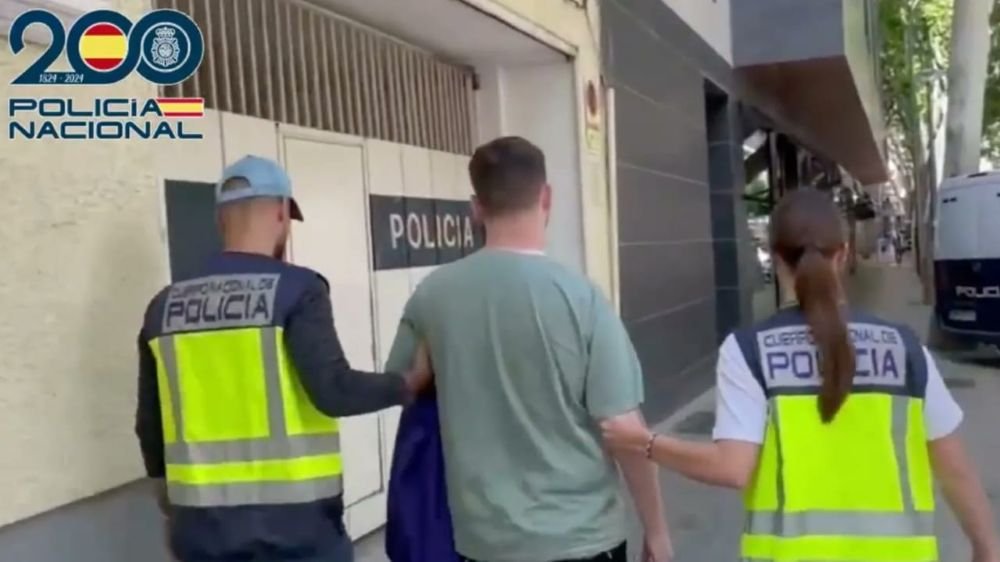

A major cybersecurity case has ended with a six-year federal prison sentence for a member of the notorious Scattered Spider cybercrime group. Tyler Robert Buchanan, a 24-year-old Scottish national, was sentenced in the United States for his involvement in a sophisticated hacking operation that targeted multiple companies and stole more than $11.6 million in cryptocurrency from victimThe case highlights the growing threat posed by organized cybercriminal networks, particularly those that exploit weaknesses in corporate security systems, steal sensitive information, and use cryptocurrency to move stolen funds. The sentence also sends a strong message about the consequences of international cybercrime, demonstrating that hackers operating across borders can still face prosecution in the United States.
Who Is Tyler Robert Buchanan?
Tyler Robert Buchanan is a Scottish national from Dundee who was involved in a cybercrime operation associated with Scattered Spider, a loosely organized hacking collective known for targeting major companies and individuals. The criminal operation took place between September 2021 and April 2023. During this period, Buchanan and his co-conspirators carried out hundreds of fraudulent text-message campaigns targeting employees at telecommunications companies, technology businesses, IT service providers, and cryptocurrency-related organizations. According to reporting on the case, the attackers compromised at least a dozen companies and used the information they obtained to identify individuals with cryptocurrency holdings. Buchanan pleaded guilty in April 2026 to conspiracy to commit wire fraud and aggravated identity theft. On November 17, 2026, he received a 72-month federal prison sentence, making him the fifth and final defendant in the case to be sentenced.
How the Scattered Spider Hackers Stole $11.6 Million in Cryptocurrency
The operation was not simply about breaking into computer systems. Instead, the hackers relied heavily on social engineering, SMS phishing, stolen login credentials, and SIM-swapping attacks to gain unauthorized access to sensitive information. Their approach involved several stages.
1. Sending Fake Text Messages to Company Employees
The attackers sent hundreds of fraudulent SMS messages to employees working at targeted organizations. These messages were designed to look like legitimate communications from employers or contracted IT support providers. Some messages reportedly warned employees about account deactivation or requested that they reset their login credentials. The messages contained links to fake websites designed to resemble genuine company login pages. Employees who entered their usernames, passwords, and personal information unknowingly handed those details to the attackers. This technique is commonly known as SMS phishing (smishing).
2. Stealing Corporate Login Credentials
Once employees submitted their information through the fraudulent websites, the hackers collected the stolen credentials. The information was reportedly transferred to a Telegram channel managed by Buchanan and another co-conspirator. With access to legitimate employee credentials, the attackers could enter company accounts and systems, obtain confidential information, and collect personal details about customers and other individuals.
3. Using SIM Swapping to Access Cryptocurrency Accounts
One of the most concerning techniques used in the operation was SIM swapping. SIM swapping is a type of identity fraud in which criminals trick a mobile network provider into transferring a victim's phone number to a SIM card or device controlled by the attacker. Once the criminals control the phone number, they may receive calls and text messages intended for the legitimate owner, including SMS-based two-factor authentication codes.nThis can allow attackers to bypass certain security protections and gain access to sensitive online accounts. Buchanan and his associates used stolen information and SIM-swapping techniques to target cryptocurrency accounts and wallets belonging to individuals across the United States. The operation ultimately resulted in the theft of at least $11.6 million in cryptocurrency.
Scattered Spider Case: What Happened to the Other Defendants?
Buchanan was not the only individual prosecuted in connection with the operation. Four other defendants were also charged and subsequently sentenced. According to reporting published following Buchanan's sentencing, the five defendants received the following prison terms:
| Defendant | Prison sentence |
|---|---|
| Noah Michael Urban | 10 years |
| Tyler Robert Buchanan | 6 years |
| Ahmed Hossam Eldin Elbadawy | 45 months |
| Evans Onyeaka Osiebo | 45 months |
| Joel Martin Evans | 2 years |
Buchanan was the fifth and final defendant to be sentenced in this case. A restitution hearing was also scheduled for December 11, 2026, to address financial compensation connected to the criminal operation.
Why the Scattered Spider Cybercrime Group Is a Serious Threat
Scattered Spider has become a widely recognized name in the cybersecurity industry because of its approach to compromising organizations. Unlike traditional cybercriminal operations that may rely primarily on malicious software or technical vulnerabilities, Scattered Spider has demonstrated how effective human manipulation can be when targeting corporate employees.
The group is associated with techniques such as:
- Phishing and SMS phishing: Sending deceptive messages to steal login credentials.
- Social engineering: Manipulating employees into revealing confidential information or granting access.
- SIM swapping: Taking control of victims' phone numbers to intercept authentication codes.
- Multi-factor authentication attacks: Exploiting weaknesses in authentication processes.
- Credential theft: Using stolen usernames and passwords to access corporate systems.
The Buchanan case demonstrates that cybersecurity threats are not limited to large organizations. Information stolen from businesses can also be used to target ordinary individuals, particularly those holding valuable digital assets. BleepingComputer
How Cryptocurrency Investors Can Protect Themselves
The theft of millions of dollars in digital assets is another reminder that cryptocurrency investors must take account security seriously. Although no security measure can guarantee complete protection, individuals can reduce their exposure to phishing and SIM-swapping attacks by following some essential precautions.
1. Use hardware security keys or passkeys.
Whenever possible, use phishing-resistant authentication methods rather than relying entirely on SMS verification codes.
2. Never click suspicious links.
Avoid clicking unexpected links in text messages, emails, or social media messages claiming that your account needs urgent verification.
3. Protect your SIM card and mobile account.
Contact your mobile provider to ask about SIM-swap protection, account PINs, and additional identity verification requirements.
4. Keep cryptocurrency seed phrases private.
Never share your recovery phrase or private keys with anyone. Store recovery information securely and offline.
5. Use separate email accounts for financial services.
A dedicated email account for cryptocurrency exchanges and financial platforms can help limit the impact of compromised personal accounts.
6. Monitor cryptocurrency transactions.
Regularly review wallet activity, exchange login notifications, and transaction histories. Report suspicious activity immediately.
7. Use strong and unique passwords.
Avoid reusing passwords across cryptocurrency exchanges, email accounts, and other online services. A reputable password manager can help.
These measures can make it significantly harder for cybercriminals to exploit stolen personal information and gain control of digital assets.
What This Case Means for the Future of Cybersecurity
The six-year prison sentence handed to Buchanan is an important development in the fight against international cybercrime. It demonstrates that cybercriminals can face serious legal consequences even when their activities involve victims, companies, and financial systems spread across different countries.
It also highlights an important lesson for businesses: investing in cybersecurity software alone is not enough. Organizations must educate employees about phishing, strengthen identity verification procedures, and introduce better protection against SIM-swapping attacks. For cryptocurrency investors, the case reinforces the importance of protecting private keys, recovery phrases, and account credentials.
As digital currencies become increasingly popular, cybercriminals will continue looking for new ways to exploit weaknesses in online security. The Scattered Spider case serves as a reminder that cybersecurity awareness and strong account protection are essential in today's digital economy.